Are you ready for CCPA? The earliest cybersecurity-audit period begins Jan. 1, 2027. Start preparing now.

Resources
  • All Resources

    Your central hub for security and compliance content.

  • Blog

    Stay informed with expert insights and practical advice on cybersecurity, privacy, and compliance challenges.

  • News

    Get the latest company updates, industry developments, and regulatory changes impacting the cybersecurity landscape.

  • Whitepapers

    Access in-depth research and strategic guidance on risk management, regulatory compliance, and cybersecurity best practices.

  • Case Studies

    See how organizations like yours solved complex cybersecurity and compliance challenges with TrustNet’s solutions.

Guides
  • All Guides

    Get practical step-by-step guides designed to help you navigate audits, improve security posture, and meet compliance requirements.

Edit Template
Logistics+ Case Study

From Compliance to Continuous Improvement: Logistics Plus and TrustNet

TL;DR 

For three consecutive years, Logistics Plus has partnered with TrustNet to build a sustainable security and compliance program, progressing from SOC 2 Type 1 to recurring SOC 2 Type 2 examinations, SOC 3 reporting, and a NIST Cybersecurity Framework (CSF) Risk Assessment.

Through a structured, collaborative approach, TrustNet has helped Logistics Plus establish a repeatable audit process, strengthen internal security practices, and demonstrate its commitment to protecting customer data. What began as a compliance requirement has evolved into an ongoing program focused on independent assurance and continuous improvement.

Background

Logistics Plus is a global logistics provider offering transportation, supply chain, and technology-enabled logistics solutions. Its operations rely on distributed, cloud-hosted systems that handle sensitive shipment, commercial, and personal data.

As customers increasingly sought independent verification of security controls rather than relying solely on questionnaires, Logistics Plus recognized the need for a more formal, sustainable approach to compliance.

The company committed to annual SOC 2 examinations to provide customers, partners, and leadership with objective assurance that its security controls were consistently maintained and evaluated.

The Challenge

With a lean IT team managing a distributed technology environment, Logistics Plus needed an audit partner that could deliver rigorous, independent examinations without disrupting daily operations.

The company sought a structured and predictable process, practical guidance, and consistency across annual engagements. More importantly, it wanted the assessments to generate meaningful improvements rather than simply satisfy compliance requirements.

The Solution: Building a Repeatable Security Program

TrustNet supported Logistics Plus through a multi-year engagement designed to strengthen security assurance while making compliance more manageable.

The partnership began with a SOC 2 Type 1 examination, establishing an initial assessment of the design of the company’s security controls. Logistics Plus subsequently progressed to recurring SOC 2 Type 2 examinations, evaluating control effectiveness over time, alongside SOC 3 reporting for broader stakeholder use.
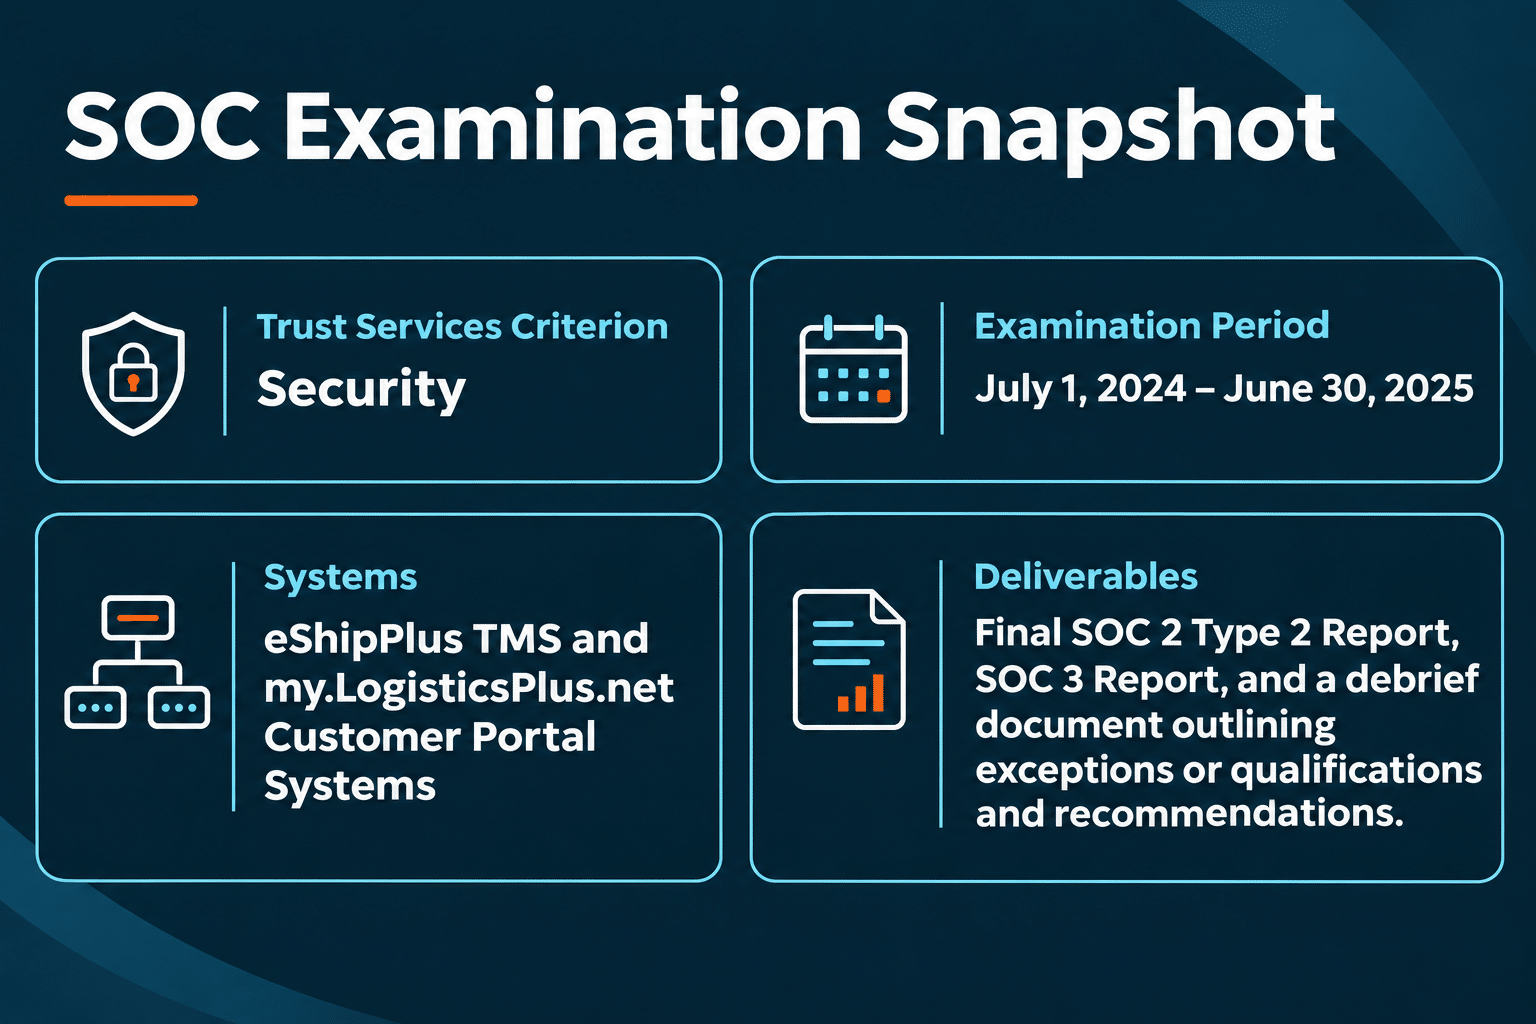
SOC examination snapshot. Trust Services Criterion: Security. Systems: eShipPlus TMS and my.LogisticsPlus.net Customer Portal Systems. Examination Period: July 1, 2024 – June 30, 2025. Deliverables: Final SOC 2 Type 2 Report, SOC 3 Report, and a debrief document outlining exceptions or qualifications and recommendations.
To streamline the process, planning documents, interview questions, and evidence requests were staged in advance through TrustCenter and Hyperproof. This allowed Logistics Plus’ IT team to prepare on its own schedule, minimizing disruption and establishing a consistent annual audit rhythm.

In 2026, the partnership expanded to include a NIST CSF Risk Assessment, providing a broader evaluation of the organization’s cybersecurity maturity.

Completed in June 2026, the assessment included a detailed spreadsheet mapping NIST CSF categories and subcategories against existing controls, risk ratings, maturity tiers, gaps, and recommendations, alongside a summary report highlighting improvement opportunities.

Together, these engagements provided Logistics Plus with both independent assurance and a structured approach to identifying and addressing cybersecurity risks.
The Results: Beyond the Audit

Over three years, Logistics Plus has transformed compliance from an annual obligation into a repeatable security discipline.

The structured audit process has made evidence collection and preparation more predictable, helping its lean IT team manage recurring examinations with less operational disruption.

Annual assessments have also encouraged the organization to regularly revisit policies, incident response plans, and internal controls, reinforcing continuous improvement rather than one-time compliance.

SOC 2 and SOC 3 reporting have provided a common language for communicating security practices to customers, partners, and leadership, while the NIST CSF assessment has added visibility into cybersecurity maturity and opportunities for improvement.

Beyond the formal deliverables, the partnership has led to practical changes in tools and processes.

“We made it very clear we do not want an audit just for an audit. We wanted it as serious as possible, to get practical value. TrustNet found a way to provide support and preparation services that doesn’t have a conflict with auditing. Knowing we’re in good hands to prepare us for the audit and knowing that they know what they’re doing, was good and comforting.”

– Emile Zafirov, CIO, Logistics Plus

For Logistics Plus, the value of working with TrustNet extends beyond successful examinations. The partnership has helped establish a sustainable approach to security, one that supports customer confidence, operational consistency, and continued improvement as the business evolves.

As of this case study’s publication, Logistics Plus is currently in the final stages of its SOC 2 Type 2 audit for the period of July 1, 2025 to June 30, 2026.

Previous Post

Get Cybersecurity Consultation

For business teams improving security and compliance

Take the first step toward CCPA compliance

Get Ready for CCPA Cybersecurity Audits

Enter your work email and our team can help you understand your requirements, assess readiness, and determine the right next steps.

TrustNet team member will follow up to discuss your needs.